FBI removes Accenture contractor after PeopleSoft breach exposes employee data
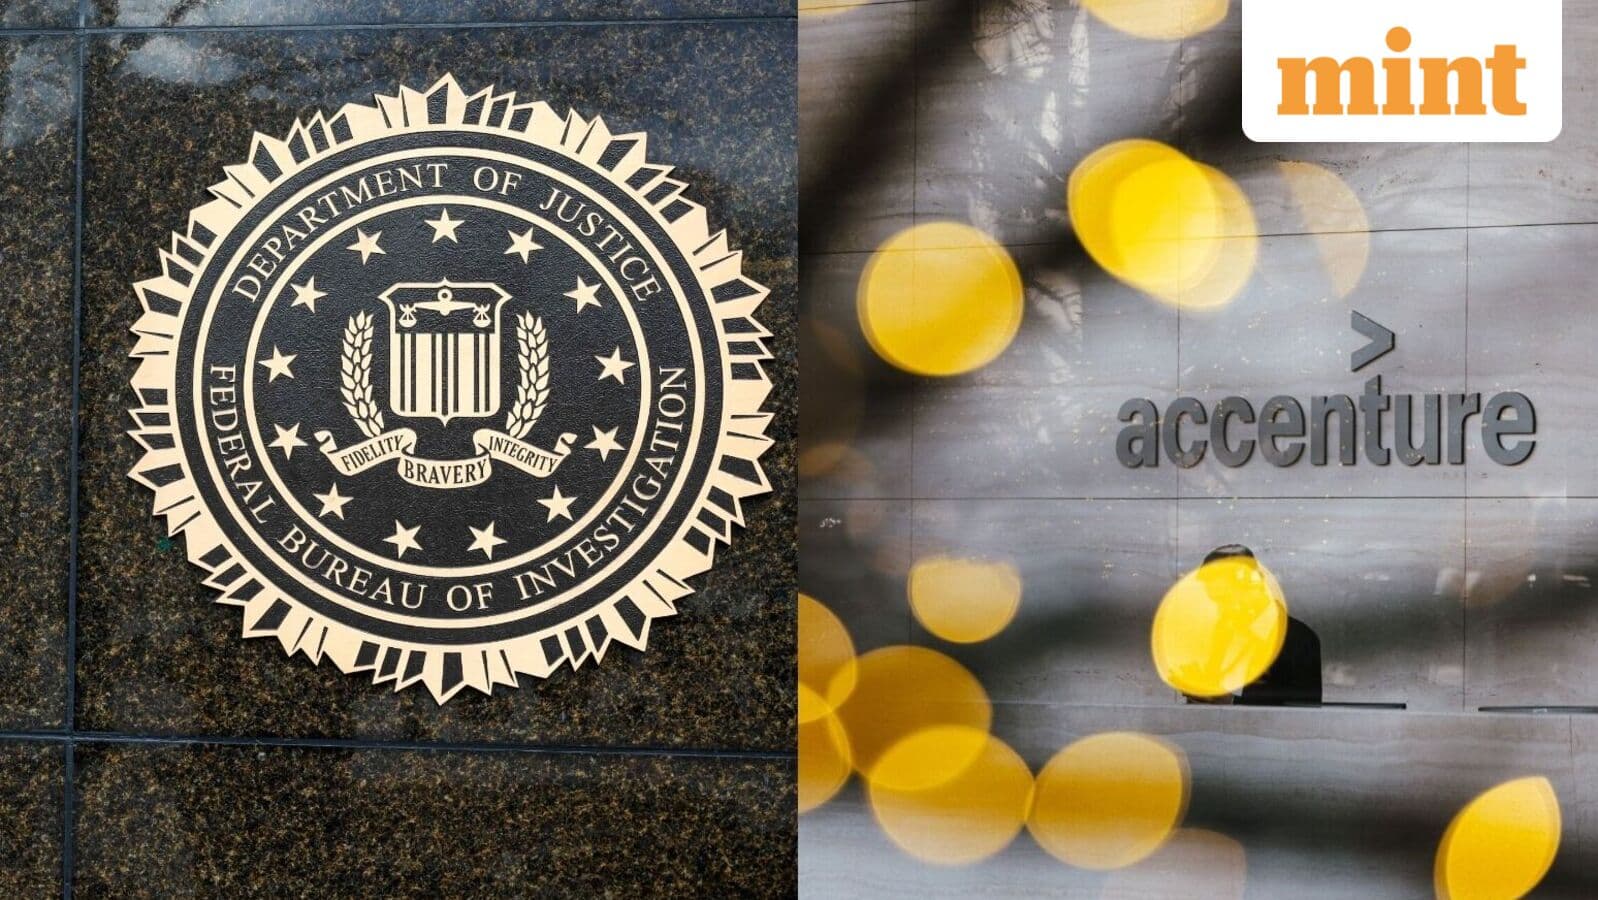
The FBI removed an Accenture contractor this week after a data breach exposed sensitive personal details of thousands of its employees. The breach, attributed to an unpatched vulnerability in Oracle’s PeopleSoft platform, was exploited by the hacking group ShinyHunters. The incident raises questions about third-party security practices and the risks of delayed software updates.

Editor, Lazyfounder
The FBI removed an Accenture contractor this week after a data breach exposed sensitive personal details of thousands of its employees. The breach, attributed to an unpatched vulnerability in Oracle’s PeopleSoft platform, was exploited by the hacking group ShinyHunters. The incident raises questions about third-party security practices and the risks of delayed software updates.
30 SEC SUMMARY
- The FBI removed an Accenture contractor after a data breach exposed sensitive personal details of thousands of FBI employees.
- The breach occurred due to a failure to implement a security patch for Oracle’s PeopleSoft platform.
- Hacking group ShinyHunters exploited the vulnerability, accessing job details, addresses, and medical records.
- Google and Oracle had previously warned about PeopleSoft vulnerabilities and urged immediate patching.
- The FBI is taking steps to mitigate further risk and protect its workforce.
TABLE OF CONTENTS
- Contractor removal and breach details
- Vulnerability and warnings
- Background
- What this means
- Key takeaways
- FAQ
- Sources
KEY HIGHLIGHTS
- The FBI removed an Accenture contractor over a data breach exposing sensitive details of thousands of employees.
- The breach was caused by a failure to implement a security patch for Oracle’s PeopleSoft platform.
- ShinyHunters exploited the vulnerability, accessing job descriptions, addresses, and medical records.
- Google and Oracle had previously warned organizations to apply critical security patches for PeopleSoft.
- The FBI is mitigating further risk and protecting its workforce following the incident.
Contractor removal and breach details
According to Mint (Technology), the FBI removed an Accenture contractor on Monday due to their alleged role in a data breach that exposed sensitive personal details of thousands of FBI employees. The contractor failed to implement a critical security patch for Oracle’s PeopleSoft platform, which was later exploited by the hacking group ShinyHunters.
The exposed data included granular job descriptions, street addresses of employees, and medical and psychiatric records. The breach affected FBI personnel involved in counterintelligence and human intelligence roles, raising concerns about operational security.
Vulnerability and warnings
The breach was linked to a known vulnerability in Oracle’s PeopleSoft platform, a widely used human resources software. Oracle had issued a security alert identifying the weakness and provided fixes, while Google also warned organizations in June about a ShinyHunters-led campaign targeting unpatched PeopleSoft systems.
Both companies urged organizations running PeopleSoft to apply all critical security patches immediately. The FBI’s failure to do so reportedly created the opening ShinyHunters exploited.
Background
The FBI has previously faced cybersecurity incidents, including a recent breach of its job application portal that exposed sensitive employee data. This pattern highlights ongoing challenges in securing government systems against evolving threats.
Oracle, the developer of PeopleSoft, has been part of broader industry layoffs, with U.S. tech companies cutting thousands of jobs in recent months. Despite these challenges, enterprise software security remains a critical concern for organizations relying on third-party platforms.
What this means
Lazyfounder analysis — our interpretation, not reported fact.
This breach underscores the critical risks of third-party contractors in managing sensitive government systems. For founders and operators, it’s a stark reminder that even well-resourced organizations can be vulnerable if basic security practices—like patch management—are overlooked. The incident also highlights the cascading consequences of software vulnerabilities, especially in widely used enterprise platforms like PeopleSoft. Startups handling sensitive data should prioritize vendor security audits, enforce strict patch management protocols, and assume that threats like ShinyHunters are actively probing for weaknesses.
Key takeaways
- The FBI’s breach was caused by a contractor’s failure to apply a critical security patch for Oracle PeopleSoft.
- Sensitive data, including job descriptions, addresses, and medical records of FBI employees, was exposed.
- ShinyHunters, a known hacking group, exploited the vulnerability after warnings from Google and Oracle.
- Third-party risk remains a significant vulnerability for organizations, including government agencies.
- Proactive patch management and vendor oversight are essential to preventing such breaches.
FAQ
What caused the FBI data breach?
The breach was caused by a failure to implement a security patch for Oracle’s PeopleSoft platform, which was managed by an Accenture contractor. The hacking group ShinyHunters exploited this vulnerability.
What data was exposed in the breach?
The breach exposed sensitive personal information of thousands of FBI employees, including job descriptions, addresses, medical records, and details about counterintelligence and human intelligence roles.
Who is responsible for the breach?
An Accenture contractor was removed by the FBI for failing to apply a critical security patch to Oracle’s PeopleSoft platform, which led to the breach.
What is ShinyHunters?
ShinyHunters is a hacking group known for exploiting vulnerabilities in enterprise software, including Oracle’s PeopleSoft. They have been linked to multiple data breaches and extortion campaigns.
How can organizations prevent similar breaches?
Organizations can reduce risks by enforcing strict patch management protocols, conducting regular security audits of third-party vendors, and applying critical security updates without delay.
Related on Lazyfounder
Sources
- Mint (Technology) · 2026-10-06
FBI removes Accenture contractor for alleged involvement in a data breach that exposed details of thousands of employees
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.
About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.