
FBI, European authorities seize Virtualine bulletproof hosting infrastructure linked to cybercrime
The FBI, alongside German and Dutch authorities, has seized the infrastructure of Virtualine, a bulletproof hosting service accused of enabling cybercrime, including ransomware, phishing, illicit cryptocurrency transactions, and child exploitation content. The operation targeted servers in Limburg and accessed data on over 3,000 customers.

Editor, Lazyfounder
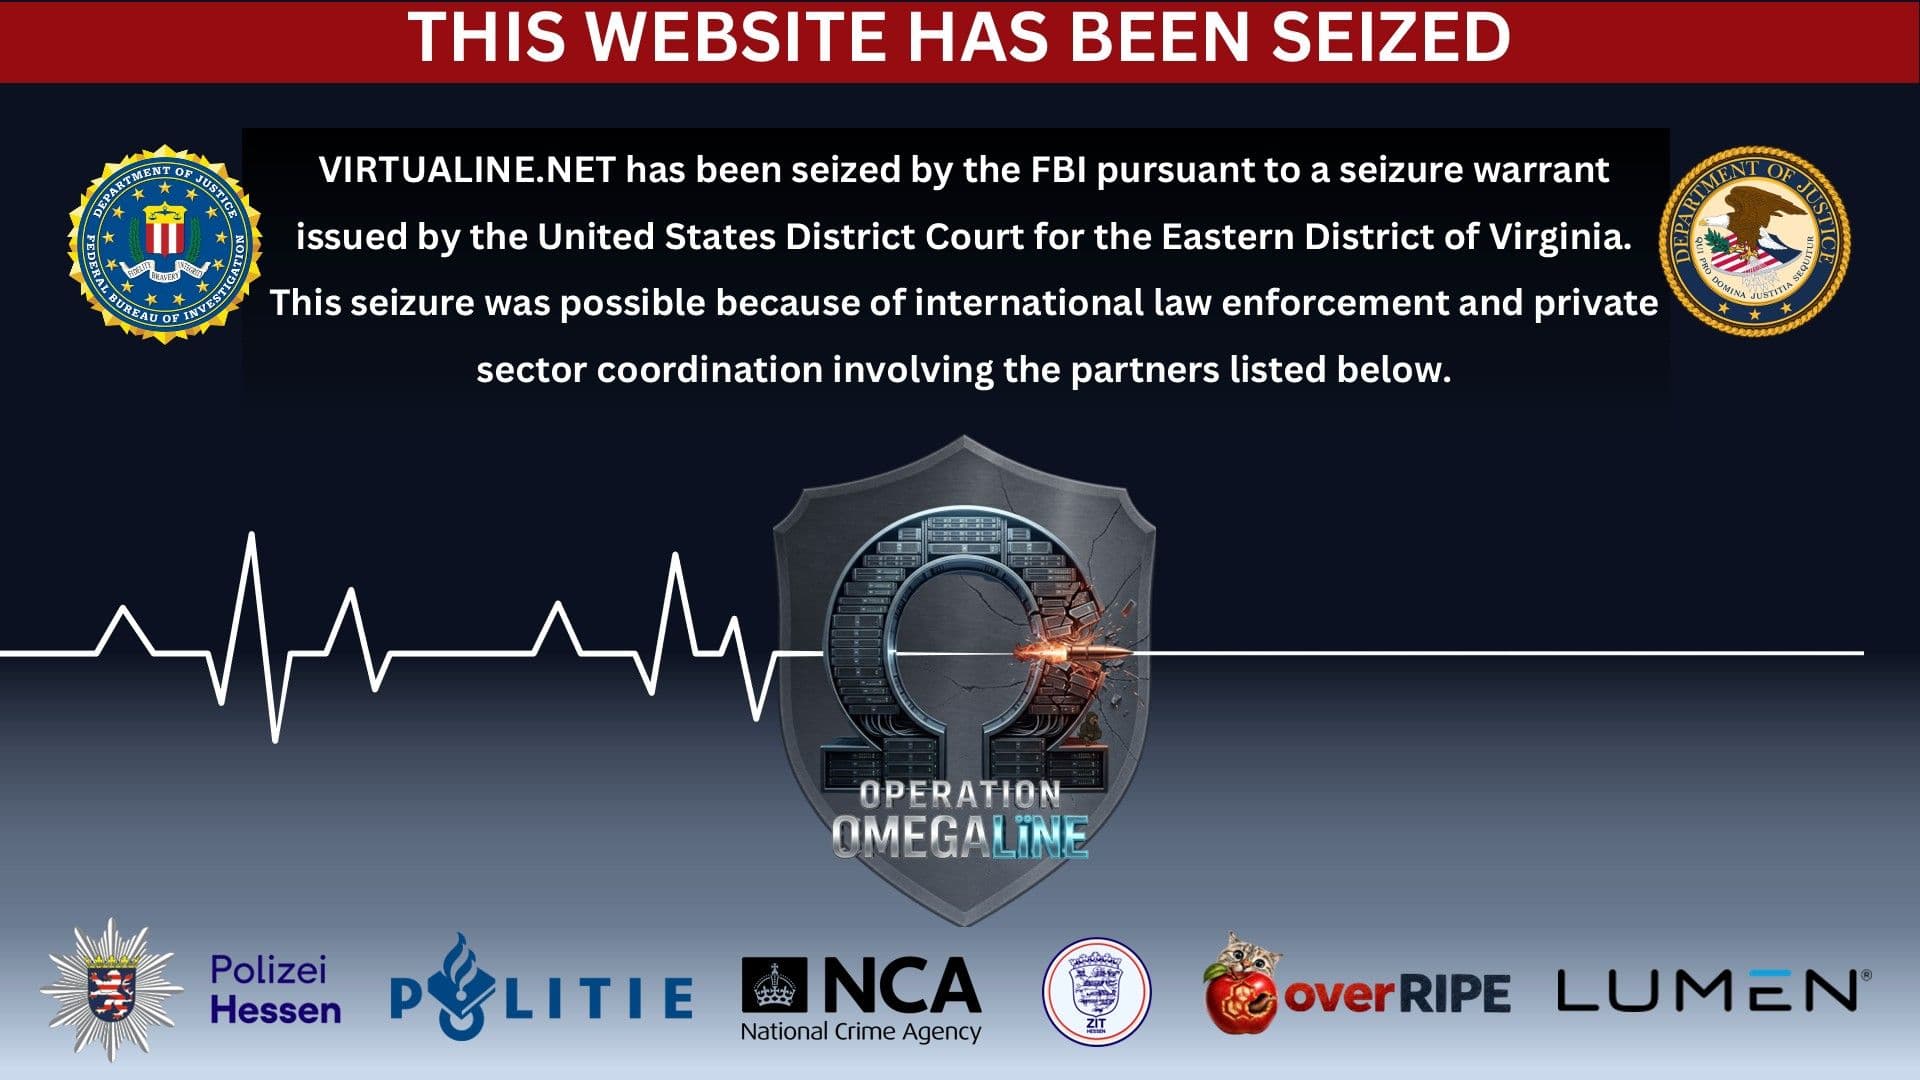
TABLE OF CONTENTS
Operation targets bulletproof hosting for cybercrime
The FBI, in coordination with German and Dutch law enforcement, has seized the infrastructure of Virtualine, a hosting service marketed as "bulletproof" for its resistance to takedown requests. Bulletproof hosting providers are known for tolerating illegal activity, and Virtualine allegedly catered to cybercriminals involved in phishing, ransomware, illicit cryptocurrency transactions, and child exploitation content.
According to reports, the service advertised its resilience to law enforcement pressure on cybercrime forums, explicitly excluding only terrorism and child exploitation content from its acceptable use—though evidence suggests it hosted the latter regardless. Authorities raided a data center in Limburg, seizing dozens of physical servers and hundreds of virtual servers.
Customer data accessed, but service remains partially online
Law enforcement accessed data on more than 3,000 Virtualine customers, though no arrests have been announced. The operation included the seizure of Virtualine’s website, which was replaced with an FBI notice. However, portions of the service’s infrastructure remain online, albeit with reduced visibility, raising concerns that it could resume full operations.
In March 2026, Virtualine introduced an "additional protection plan" to help customers evade takedown requests, further insulating its operations from legal scrutiny. Authorities reported that the service ignored repeated warnings about illegal content, including child exploitation material and ransomware operations.
Cryptocurrency laundering and ransomware ties
Virtualine’s Bitcoin wallet reportedly received funds from ransomware operations, infostealers, and Russian-language cybercrime forums, according to the operation’s findings. The service allowed customers to pay in cryptocurrency, facilitating the laundering of proceeds from cybercrime.
Bulletproof hosting services like Virtualine are often used by threat actors to host command-and-control servers for ransomware attacks, phishing pages, and other malicious infrastructure. Their resilience to legal pressure makes them attractive to criminals, though disruptions like this are intended to degrade their operations.
Recent law enforcement cooperation in cybercrime
This operation follows recent collaborative efforts between US and European authorities to dismantle cybercrime infrastructure. Earlier reporting highlighted the arrest of an alleged leader of the ShinyHunters hacking group by Dutch police, working alongside the FBI. That case also involved international coordination to address high-profile data breaches and cyber threats.
Cybercrime operations increasingly rely on bulletproof hosting to evade detection and takedowns. The seizure of Virtualine underscores the challenges authorities face in permanently shutting down such services, which often resume activity under new domains or infrastructure.
What this means
Lazyfounder analysis — our interpretation, not reported fact.
The takedown of Virtualine is a rare but significant disruption of a service designed to shield cybercriminals from legal consequences. For founders and operators, this serves as a reminder of how critical it is to monitor where malicious actors host their infrastructure—especially if their own platforms or users are targeted by phishing, ransomware, or other attacks. While bulletproof hosting services are notoriously difficult to shutter permanently, operations like this degrade their reliability, forcing cybercriminals to rebuild or relocate, which can temporarily reduce their effectiveness. However, the partial survival of Virtualine’s infrastructure also highlights the limitations of even well-coordinated enforcement actions.
Related on Lazyfounder
Sources
- TechRadar · 2026-10-29
FBI leads action to shut down Virtualine bulletproof service linked to major cybercrime activity
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.

About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.
