Oracle Embeds Security Controls into Databases to Counter AI Threats
Oracle Corp. has launched a new security strategy called "Secure at Source," which embeds security controls like encryption and access restrictions directly into databases. The approach is designed to address vulnerabilities introduced by AI agents and indirect access paths, ensuring protections are enforced at the data layer itself.
LazyFounders
Oracle Corp. has launched a new security strategy called "Secure at Source," which embeds security controls like encryption and access restrictions directly into databases. The approach is designed to address vulnerabilities introduced by AI agents and indirect access paths, ensuring protections are enforced at the data layer itself.
30 SEC SUMMARY
- Oracle introduces "Secure at Source," a strategy embedding security controls like encryption and access restrictions directly into databases.
- The approach aims to counter risks from AI agents bypassing application-level security measures.
- Oracle Data Safe and Oracle Database Security Central provide fleet-wide security visibility.
- Fleet-wide monitoring helps detect configuration drift, excessive privileges, and policy inconsistencies.
- Oracle’s strategy combines centralized posture management with real-time database protections.
TABLE OF CONTENTS
- Oracle Moves Security Controls to the Database Layer
- Countering AI-Driven Threats with Database-Level Security
- Fleet-Wide Visibility for Proactive Security
- A Comprehensive Approach to Database Security
- The Broader Context: AI and Data Security
- What this means
- Key takeaways
- FAQ
- Sources
KEY HIGHLIGHTS
- Oracle launches "Secure at Source," embedding security controls directly within databases.
- The strategy prevents unauthorized access even when AI agents bypass application-level security.
- Oracle Data Safe and Oracle Database Security Central provide fleet-wide security visibility.
- Fleet-wide monitoring helps detect configuration drift, excessive privileges, and policy gaps.
- Oracle combines centralized posture management with real-time database protections.
Oracle Moves Security Controls to the Database Layer
Oracle Corp. has introduced a new security strategy called "Secure at Source," which moves core security controls—such as encryption and access restrictions—directly into the database layer. According to SiliconANGLE, this approach aims to reduce dependence on individual applications to enforce security, a model that becomes increasingly vulnerable as AI agents create new access pathways to enterprise data.
Countering AI-Driven Threats with Database-Level Security
The "Secure at Source" strategy ensures that authorization and access controls are enforced regardless of how users or AI agents interact with the database. SiliconANGLE reports that Oracle demonstrated how indirect prompts, designed to bypass application guardrails, could expose sensitive data like salary information unless restrictions are embedded within the database itself.
By enforcing these rules at the database level, Oracle claims it can prevent unauthorized data retrieval even when application-level security fails.
Fleet-Wide Visibility for Proactive Security
Oracle’s latest tools, Oracle Data Safe and Oracle Database Security Central, are designed to provide fleet-wide visibility into security posture across an organization’s database environment. SiliconANGLE notes that these tools help identify configuration drift, excessive privileges, and inconsistent policies before they can be exploited.
Oracle Data Safe offers cloud-based security assessments and monitoring, while Oracle Database Security Central delivers a unified view of users, sensitive data, configurations, and policies across an entire database fleet.
A Comprehensive Approach to Database Security
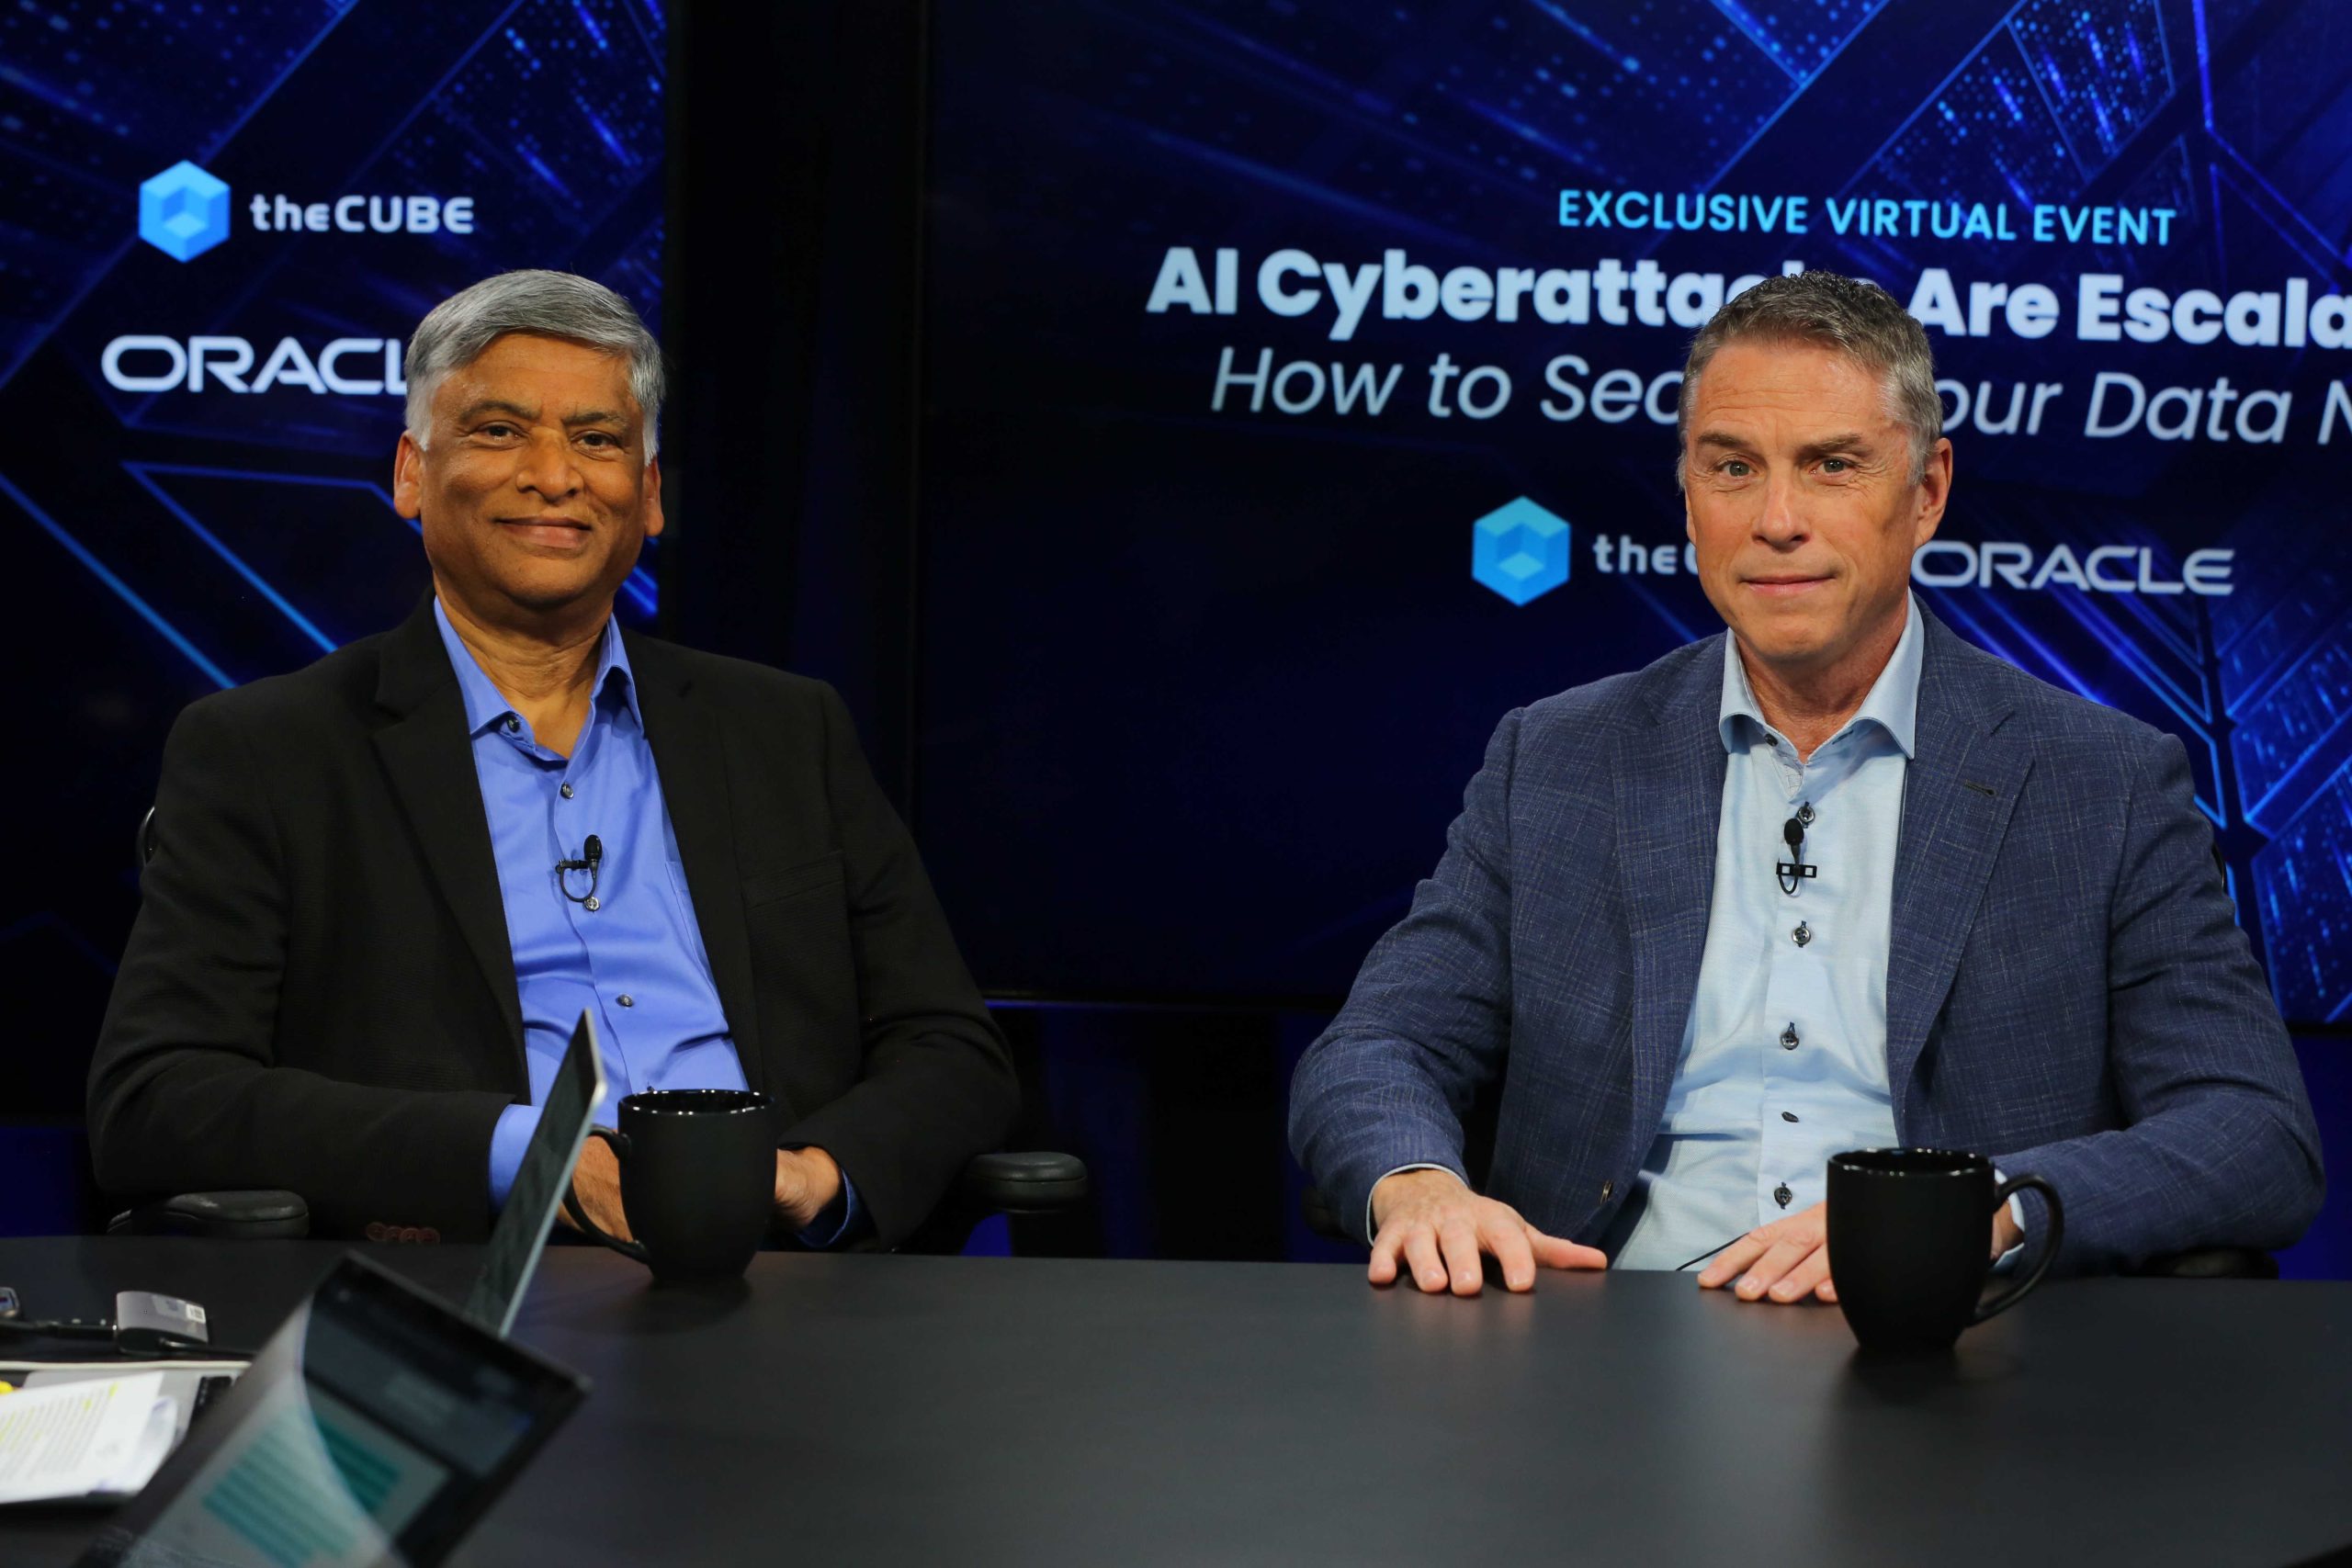
Vipin Samar, Oracle’s Senior Vice President of Database Security, emphasized that security extends beyond encryption. It requires a comprehensive approach, including access controls, patching, and centralized visibility to effectively protect enterprise data.
Oracle’s updated portfolio combines these elements, applying centralized posture management alongside real-time protections during database access.
The Broader Context: AI and Data Security
The rise of AI-driven threats has exposed limitations in traditional security models, which often rely on application-layer protections. As AI agents create indirect access paths to data, securing the database itself becomes a critical defense.
Recent developments in cybersecurity, such as Vicarius’ ScriptAI for automating fixes to unpatched vulnerabilities, reflect a broader industry push to address evolving threats. Oracle’s approach, however, focuses on preemptive security by embedding controls at the source.
What this means
LazyFounders analysis — our interpretation, not reported fact.
Oracle’s shift to "Secure at Source" highlights a critical gap in traditional security models: as AI agents and indirect access paths proliferate, relying solely on application-layer protections is no longer enough. For founders and operators, this signals a need to rethink security architectures—especially if their products interact with sensitive data or AI-driven workflows.
Embedding security at the database layer could reduce risks like unauthorized data exposure, but it also introduces complexity. Teams will need to ensure that performance, usability, and compliance aren’t compromised in the process. Tools like Oracle’s fleet-wide monitoring solutions may become essential for enterprises managing sprawling database environments, as they offer a way to preemptively address misconfigurations and privilege sprawl.
Key takeaways
- Oracle’s "Secure at Source" embeds security controls directly into databases, reducing reliance on application-layer protections.
- The strategy addresses threats from AI agents bypassing traditional guardrails.
- Oracle Data Safe and Oracle Database Security Central offer centralized security monitoring for database fleets.
- Fleet-wide visibility helps identify risks like configuration drift and excessive privileges before exploitation.
- This approach combines centralized posture management with real-time protections during database access.
FAQ
What is Oracle’s "Secure at Source" strategy?
It is a security approach that embeds controls like encryption and access restrictions directly into databases, rather than relying on applications to enforce security.
How does this strategy address threats from AI agents?
By enforcing security at the database level, Oracle aims to prevent unauthorized access even when AI agents bypass application-level guardrails.
What tools has Oracle introduced to support this strategy?
Oracle Data Safe and Oracle Database Security Central provide fleet-wide visibility into security posture, helping identify issues like configuration drift and excessive privileges.
Why is fleet-wide visibility important for database security?
It allows organizations to monitor and address security gaps—such as inconsistent policies or excessive privileges—across their entire database fleet before they can be exploited.
Related on LazyFounders
Sources
- SiliconANGLE · 2026-09-23
Oracle puts database security controls beneath AI agents
This story is an original summary and analysis written by LazyFounders from the reporting listed above. Facts are attributed to their original publishers; sections marked as analysis are LazyFounders's opinion. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links.