
TFG London and H&M investigate separate cyber-security incidents
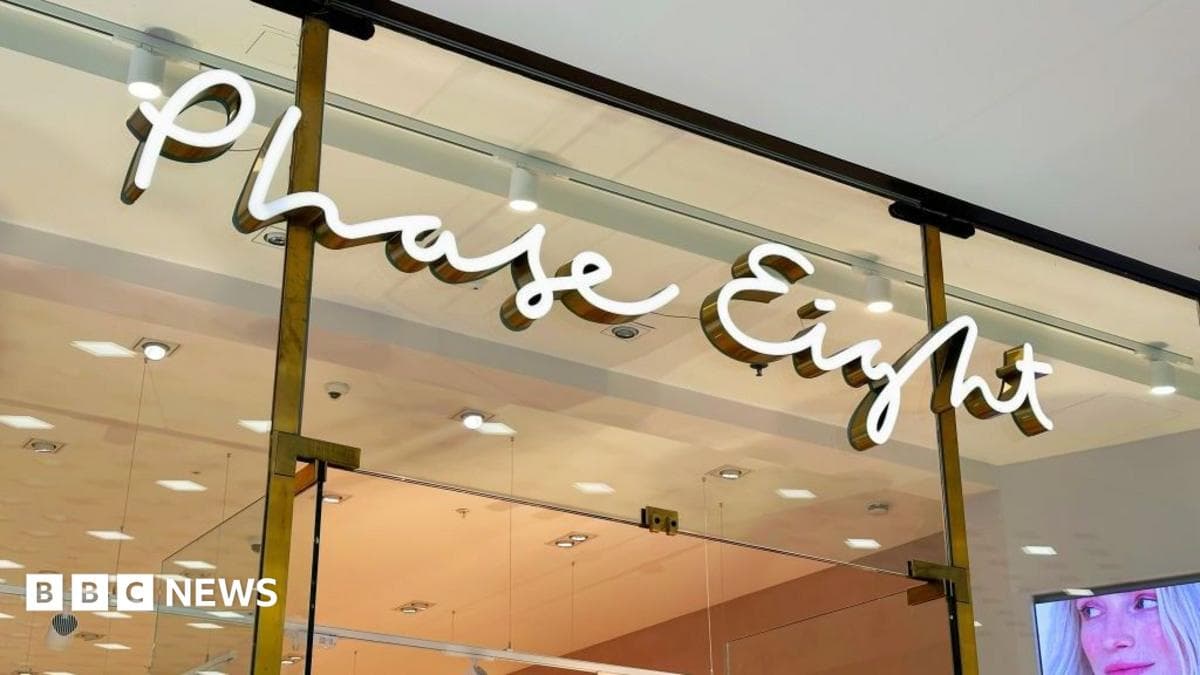
TFG London, the UK arm of The Foschini Group, is investigating a cyber-security incident affecting its IT systems, particularly for brands like Phase Eight, Hobbs, and Whistles. Meanwhile, H&M is probing a separate claim of a cyber-attack by a hacking group. These incidents underscore the fashion industry’s growing vulnerability to cyber-extortion and data breaches.

Editor, Lazyfounder
30 SEC SUMMARY
- TFG London, the UK arm of South Africa’s The Foschini Group and owner of brands like Phase Eight, Hobbs, and Whistles, is investigating a cyber-security incident affecting its IT systems.
- The incident was identified on Sunday and may impact website functionality, though stores remain operational.
- H&M is separately probing claims of a cyber-attack by a notorious hacking group.
- Cyber-attacks on fashion brands often involve extortion attempts, as seen with Adidas and Alexander McQueen.
- Customers are advised to remain vigilant for suspicious messages amid these incidents.
TABLE OF CONTENTS
KEY HIGHLIGHTS
- TFG London detected a cyber-security incident on Sunday, affecting IT systems for brands Phase Eight, Hobbs, and Whistles.
- Stores are operating normally, but some website capabilities may be unavailable.
- TFG London does not believe customer payment information has been compromised but is investigating potential data impacts.
- H&M is investigating a separate claim of a cyber-attack by a hacking group.
- Recent cyber-attacks on fashion brands like Adidas and Alexander McQueen have involved ransom demands.
Cyber-security incident disrupts TFG London’s IT systems
TFG London, the UK subsidiary of South African retail conglomerate The Foschini Group, is investigating a cyber-security incident that disrupted some of its IT systems. According to BBC News, the incident was identified on Sunday and has specifically affected the Phase Eight, Hobbs, and Whistles brands.
TFG London stated that its stores continue to operate as usual, though certain website functionalities may be temporarily unavailable. The company added that it does not believe customers’ payment information has been compromised. However, it is still assessing whether sensitive customer data has been impacted and will notify affected individuals directly if necessary.
H&M probes separate cyber-attack claim
H&M is investigating a separate claim that it was targeted by a notorious hacking group, BBC News reports. The company has not yet confirmed the extent or impact of the alleged attack.
Fashion industry faces rising cyber-extortion threats
Cyber-criminals have increasingly targeted fashion brands, using ransom demands to extort money. Recent attacks on companies like Adidas and Alexander McQueen highlight the growing threat to the sector. According to BBC News, such incidents often involve demands for payment in exchange for restoring access to compromised systems or preventing data leaks.
Beverley Griffiths, Senior Lecturer in Security and Resilience at Bucks New University, reportedly advised customers to remain vigilant and cautious of suspicious messages, particularly those claiming to be from affected brands.
Context on recent cyber-attacks in retail
The fashion and retail sectors have seen a surge in cyber-attacks, with hackers often targeting large brands to extract sensitive data or disrupt operations. Recent incidents involving companies like Adidas and Alexander McQueen have demonstrated the financial and reputational risks of such breaches. These attacks frequently involve ransomware, where hackers encrypt critical data and demand payment for its release.
What this means
Lazyfounder analysis — our interpretation, not reported fact.
For founders and operators in retail and fashion, these incidents are a stark reminder of the vulnerabilities in digital infrastructure. Even if payment systems remain secure, the potential exposure of customer data can erode trust and trigger regulatory scrutiny. The fact that two major retailers are investigating incidents simultaneously suggests that cyber-criminals are either coordinating attacks or exploiting common weaknesses in the sector’s defenses.
Proactive measures—such as regular security audits, employee training, and incident response plans—are no longer optional. Companies must also consider how they communicate with customers during a breach. Transparency and speed are critical to mitigating reputational damage, but they require preparation. If TFG London or H&M confirm data exposure, the fallout could include not just financial costs but also long-term brand erosion.
Key takeaways
- Cyber-security incidents can disrupt operations even if core systems like payments remain unaffected, highlighting the need for robust IT resilience.
- Retailers must prioritize transparent communication with customers during breaches to maintain trust and comply with regulatory requirements.
- The fashion industry is a prime target for cyber-extortion, so founders should invest in preventive measures like security audits and employee training.
- Incident response plans are essential to minimize damage, as delays or unclear messaging can amplify reputational harm.
- Even if payment data is secure, the exposure of personal customer information can lead to regulatory penalties and customer attrition.
FAQ
What brands are affected by TFG London’s cyber-security incident?
The incident has impacted Phase Eight, Hobbs, and Whistles, all of which are owned by TFG London.
Are TFG London’s stores still open?
Yes, TFG London confirmed that its stores are operating normally, though some website functionalities may be unavailable.
Has customer payment information been compromised in the TFG London incident?
TFG London does not believe payment information has been affected, but it is still investigating potential impacts on other sensitive customer data.
What should customers do if they suspect fraudulent activity?
Customers are advised to stay vigilant for suspicious messages, such as phishing emails or texts, and report any unusual activity to the relevant brand or their bank.
Related on Lazyfounder
Sources
- BBC News (Tech & Business) · 2026-10-13
Phase Eight owner hit by cyber-attack as H&M probes separate hack claim
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.
About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.
