Maersk confirms data breach in LF Logistics legacy system, hackers demand $5M
A.P. Moller–Maersk, the global shipping and logistics operator, confirmed a data breach in a legacy system inherited from its 2022 acquisition of LF Logistics. Hackers are demanding a $5 million ransom, threatening to release 100GB of stolen data, including sensitive records and plaintext passwords. Maersk says its core operations remain secure.

Editor, Lazyfounder
Breach targets inherited legacy system
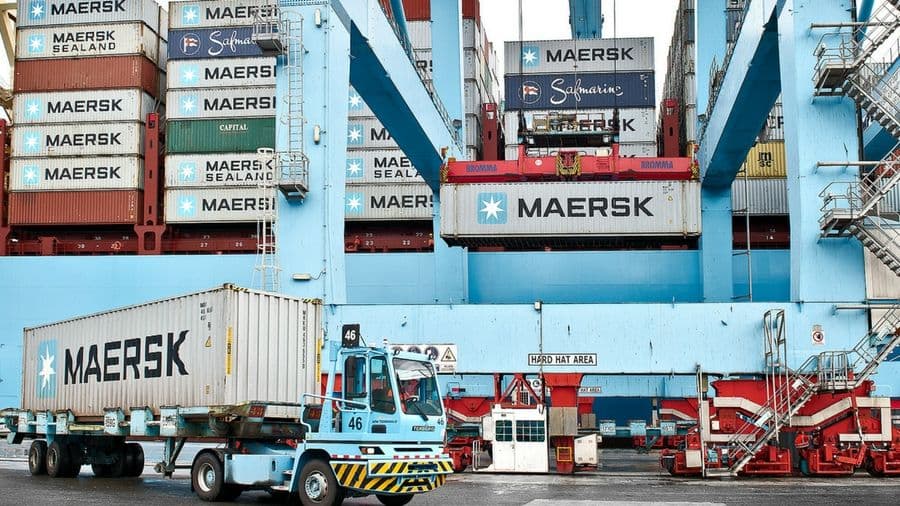
A.P. Moller–Maersk confirmed a data breach affecting a legacy system tied to its 2022 acquisition of Hong Kong-based LF Logistics. The attack, attributed to the hacking group WhiteArmor, involves 100GB of stolen data, including driver records, plaintext passwords, and logistics information.
$5M ransom demand and operational impact
WhiteArmor has demanded a $5 million ransom in bitcoin, threatening to leak the stolen data within 30 days. The group claims to hold sensitive records, including 27,842 mobile device logs with phone numbers, email addresses, and IMEI numbers, along with 33 SUPER_ADMIN accounts and signed delivery receipts.
Maersk stated that its core operations remain unaffected and no sensitive data has been disclosed so far. The company is investigating the breach while continuing normal shipping and logistics services for customers.
Acquisition history and past cyber incidents
Maersk’s acquisition of LF Logistics in 2022 for $3.6 billion expanded its global logistics division, incorporating warehousing and ecommerce fulfillment systems. The breach highlights risks in integrating legacy IT infrastructure from acquired companies.
The company previously faced a major cyber incident in 2017, when the NotPetya attack caused $250–300 million in losses and disrupted its global network.
Key takeaways
- Maersk’s breach exposes risks tied to legacy systems inherited during acquisitions—a caution for logistics and supply-chain startups integrating third-party platforms.
- The $5 million ransom demand underscores the financial scale of cyber extortion, which may inform cybersecurity budgeting for operators in high-value industries.
- Plaintext passwords and SUPER_ADMIN accounts in the leaked data highlight critical vulnerabilities; founders should audit credential storage and access controls post-acquisition.
- Maersk’s 2017 NotPetya attack ($250–300M loss) shows how cyber incidents disrupt global operations; this breach reinforces the need for rapid containment in logistics tech.
Related on Lazyfounder
Sources
- TechRadar · 2026-11-12
Shipping giant Maersk confirms data breach as hackers demand $5 million ransom
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.
About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.