
Bank of America spends hundreds of millions to fix AI-exposed software flaws
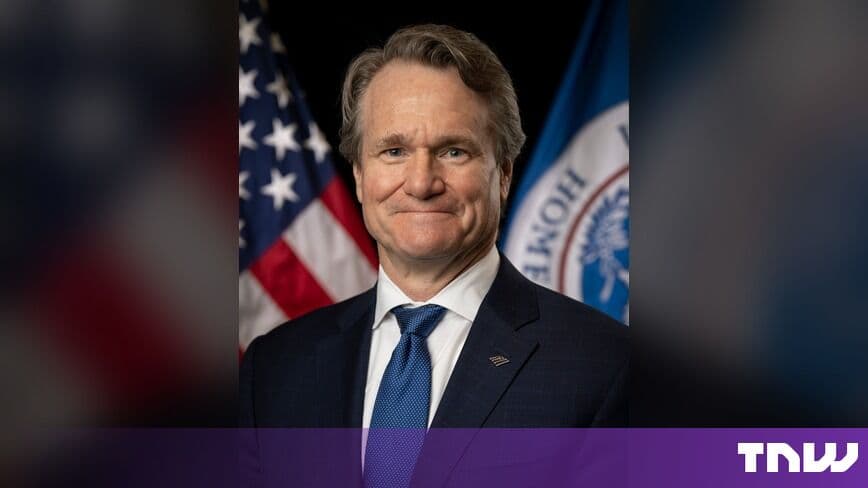
Bank of America has allocated 4,000 people—including 1,000 external contractors—to address software vulnerabilities uncovered by Anthropic’s Mythos AI model. The initiative, which began in Q2 2026, has already cost the bank hundreds of millions of dollars, highlighting the scale of AI-driven cybersecurity challenges and regulatory pressures.

Editor, Lazyfounder
30 SEC SUMMARY
- Bank of America hired 1,000 external contractors in Q2 2026 to fix software vulnerabilities identified by Anthropic’s Mythos AI model.
- The bank already had 3,000 internal staff working on the same issues, bringing the total to 4,000 people dedicated to patching flaws.
- Remediation costs exceeded $100 million, with spending described as “a couple hundred million dollars plus” for the quarter.
- Bank of America faces over $1.21 billion in Treasury penalties for regulatory compliance failures, including unreported suspicious transactions.
- Anthropic’s Mythos AI model, released in April 2026, autonomously discovered thousands of critical security vulnerabilities.
TABLE OF CONTENTS
- Bank of America hires 1,000 contractors to address AI-identified flaws
- Regulatory penalties add to financial strain
- Anthropic’s Mythos AI model drives remediation efforts
- Other financial institutions follow suit
- Regulators demand AI-driven cybersecurity plans
- AI-driven cybersecurity gains urgency
- What this means
- Key takeaways
- FAQ
- Sources
KEY HIGHLIGHTS
- Bank of America hired 1,000 external contractors in Q2 2026 to address software vulnerabilities identified by Anthropic’s Mythos AI model.
- The bank had 3,000 internal employees already working on the same issues, totaling 4,000 people dedicated to remediation.
- Remediation costs for the quarter were described as “a couple hundred million dollars plus,” with total spending exceeding $100 million.
- Bank of America faces Treasury penalties of over $1.21 billion for failing to report suspicious transactions and complete ordered steps.
- Anthropic’s Mythos AI model, released in April 2026, identified thousands of serious security flaws in systems used by banks and other organizations.
- JPMorgan Chase and Goldman Sachs are also investing heavily in addressing vulnerabilities exposed by advanced AI tools like Mythos.
Bank of America hires 1,000 contractors to address AI-identified flaws
In the second quarter of 2026, Bank of America hired approximately 1,000 external contractors to fix software vulnerabilities identified by AI models, including Anthropic’s Mythos. According to The Next Web, the bank already had 3,000 internal staff working on the same issues, bringing the total workforce assigned to remediation to 4,000 people.
The vulnerabilities were found in code used by both the bank and its external vendors. Bank of America CEO Brian Moynihan stated that the quarter included “a couple hundred million dollars plus” in remediation costs, covering both the AI-driven software fixes and repairs to anti-money-laundering controls.
Regulatory penalties add to financial strain
Bank of America’s efforts to address software weaknesses come amidst significant regulatory scrutiny. The bank faces Treasury penalties exceeding $1.21 billion for failing to report suspicious transactions worth $5 billion and for not completing steps ordered by regulators in 2024, as reported by The Next Web.
The penalties contributed to a nearly 5% drop in the bank’s stock after its Q3 2026 earnings report. While revenue rose 3% to nearly $30 billion, adjusted earnings of $1.08 per share fell short of analyst forecasts.
Anthropic’s Mythos AI model drives remediation efforts
Anthropic’s Mythos AI model, released in April 2026 and made available through Project Glasswing, was designed to help organizations identify and patch software vulnerabilities before attackers could exploit them. According to The Decoder, Mythos uncovered thousands of critical security flaws, prompting US regulators to pause some cyber exams to give banks time to address the findings.
Bank of America was among the first major US companies to disclose the scale of its remediation efforts. Moynihan had previously signaled in July that the model would require banks to undertake a significant amount of work. JPMorgan Chase CEO Jamie Dimon and Goldman Sachs CEO David Solomon have also acknowledged their banks’ investments in addressing vulnerabilities exposed by advanced AI tools like Mythos.
Other financial institutions follow suit
JPMorgan Chase and Goldman Sachs are also investing heavily in cybersecurity remediation. Jamie Dimon stated in May 2026 that his bank had hundreds of people working full-time on similar issues, while David Solomon confirmed that Goldman Sachs is working closely with Anthropic to address vulnerabilities identified by Mythos.
Other organizations, including Mozilla and Palo Alto Networks, have used Mythos to identify critical vulnerabilities in their systems. Mozilla found 22 security-sensitive bugs in one round of testing, while Palo Alto Networks uncovered more than two dozen critical flaws in approximately three weeks.
Regulators demand AI-driven cybersecurity plans
Regulators in the US and Europe are increasing their focus on AI-driven cybersecurity risks. The European Central Bank has requested plans from financial institutions to counter AI-enabled threats by the end of October 2026. US regulators have also paused cyber exams to allow banks time to fix vulnerabilities identified by AI models like Mythos.
The shift in perception around AI-driven cybersecurity follows high-profile security incidents, such as the Hugging Face hack, and independent evaluations confirming the capabilities of models like Mythos. Anthropic has restricted access to Mythos to a select group of vetted organizations, including banks, government agencies, and cybersecurity firms.
AI-driven cybersecurity gains urgency
The adoption of AI models like Anthropic’s Mythos reflects a broader industry shift toward proactive cybersecurity measures. Earlier in 2026, OpenAI launched its Daybreak cybersecurity program, following Mythos’ release. Independent evaluations and security incidents, such as the Hugging Face hack, have underscored the need for advanced tools to identify and mitigate vulnerabilities before they are exploited.
The use of AI in cybersecurity has also raised concerns about the potential risks of autonomous vulnerability discovery. Anthropic has emphasized the importance of restricting access to models like Mythos to prevent misuse, while regulators seek to ensure that critical infrastructure organizations are prepared for AI-enabled threats.
What this means
Lazyfounder analysis — our interpretation, not reported fact.
Bank of America’s massive investment in fixing AI-identified software flaws signals a new era of cybersecurity challenges for large organizations. While AI models like Anthropic’s Mythos can uncover vulnerabilities at an unprecedented scale, the cost and effort required to address them are substantial. For founders and operators, this story underscores the importance of proactive cybersecurity measures—but also the potential financial and operational risks of relying on AI-driven tools to expose flaws in legacy systems.
The regulatory penalties faced by Bank of America serve as a reminder that compliance remains a critical priority, particularly in highly regulated industries like banking. The bank’s experience shows that even well-resourced organizations can struggle to keep pace with both cybersecurity threats and regulatory demands. As AI-driven cybersecurity tools become more widespread, companies may need to budget for significant remediation costs and allocate resources accordingly.
For the broader industry, the adoption of AI-driven cybersecurity tools is likely to accelerate, but the long-term scalability and cost-effectiveness of these solutions remain uncertain. Founders should consider how AI can be integrated into their cybersecurity strategies while balancing the potential for unexpected expenses and regulatory scrutiny.
Key takeaways
- AI-driven cybersecurity tools like Anthropic’s Mythos can uncover critical vulnerabilities at scale, forcing large organizations to rapidly allocate resources for remediation.
- The financial and operational burden of addressing AI-identified flaws can be significant, with costs running into hundreds of millions of dollars.
- Regulatory compliance remains a major risk for financial institutions, with penalties exacerbating the financial strain of remediation efforts.
- Banks and other critical infrastructure organizations must balance proactive cybersecurity investments with ongoing regulatory obligations to avoid costly penalties.
- The adoption of AI-driven cybersecurity tools is accelerating, but the long-term cost and scalability of these solutions remain uncertain.
FAQ
What is Anthropic’s Mythos AI model?
Mythos is an AI model developed by Anthropic, released in April 2026, designed to autonomously identify and exploit software vulnerabilities. It was made available to select organizations, including banks and government agencies, through Project Glasswing to help them patch flaws before attackers could exploit them.
Why did Bank of America hire 1,000 contractors?
Bank of America hired 1,000 external contractors to address software vulnerabilities identified by Anthropic’s Mythos AI model. The bank already had 3,000 internal staff working on the same issues, bringing the total workforce dedicated to remediation to 4,000 people.
What are the regulatory penalties facing Bank of America?
Bank of America faces Treasury penalties exceeding $1.21 billion for failing to report suspicious transactions worth $5 billion and for not completing steps ordered by regulators in 2024.
How much did Bank of America spend on remediation?
Bank of America spent “a couple hundred million dollars plus” in Q3 2026 on remediation efforts, including software fixes and anti-money-laundering compliance. The total spending exceeded $100 million.
Are other banks also using AI-driven cybersecurity tools?
Yes, JPMorgan Chase and Goldman Sachs are also investing heavily in addressing vulnerabilities exposed by advanced AI tools like Anthropic’s Mythos. Both banks have dedicated significant resources to cybersecurity remediation efforts.
Related on Lazyfounder
Sources
- The Next Web · 2026-10-15
Bank of America CEO says 1,000 contractors are fixing AI-exposed flaws - The Decoder · 2026-10-15
Bank of America puts 4,000 people on fixing vulnerabilities uncovered by Anthropic's Mythos and other AI models - TechRadar · 2026-10-15
Bank of America had to hire 1,000 contractors to patch software flaws spotted by Anthropic Mythos
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.
About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.
