
AU Small Finance Bank probes alleged data breach via Salesforce app
AU Small Finance Bank is examining claims by hackers known as ScarlettGroup that they accessed sensitive customer and internal records, including Aadhaar, PAN numbers, and financial documents, through its Salesforce app. The bank confirmed a potential breach on the platform but stated its core banking systems remain secure.

Editor, Lazyfounder
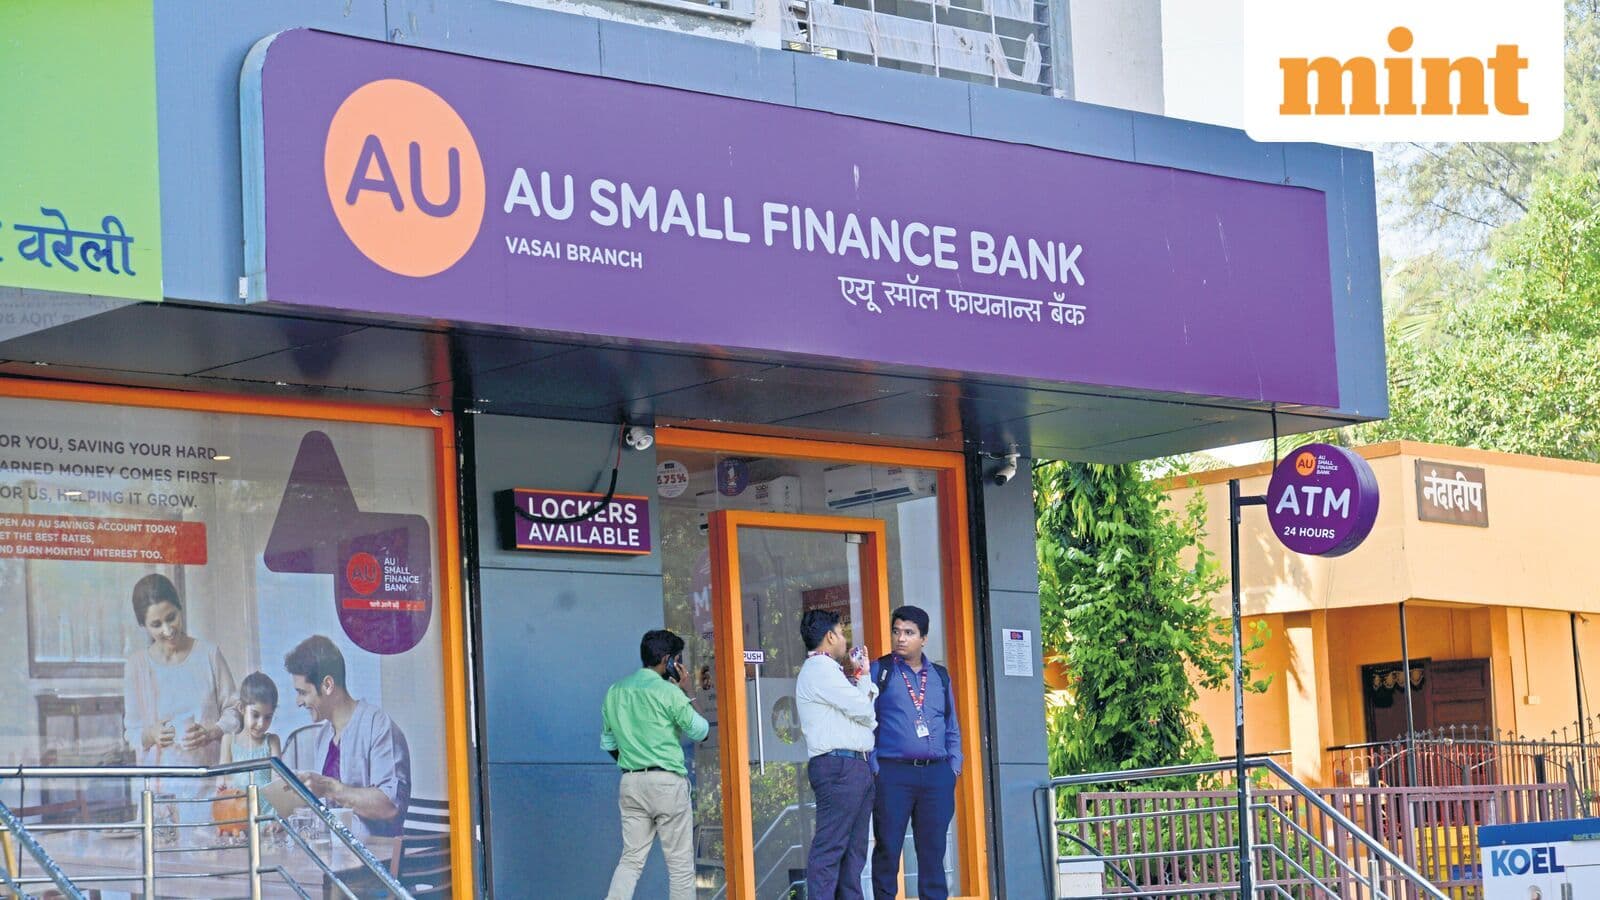
TABLE OF CONTENTS
What happened
AU Small Finance Bank is investigating a potential data breach after a hacker group identified as ScarlettGroup claimed to have accessed sensitive customer and internal records. The group alleged the breach involves Aadhaar and PAN numbers, KYC documents, CIBIL scores, bank statements, loan approvals, insurance records, and internal company data such as employee directories and audit logs.
The breach was first highlighted by cybersecurity monitoring account H4ckmanac on X (formerly Twitter) on October 30, 2026. ScarlettGroup published a countdown labeled "Negotiation deadline" and displayed blurred samples of documents, threatening to leak the data if negotiations are not met within six days. The claims remain unverified.
Bank’s response
AU Small Finance Bank acknowledged a potential breach on its Salesforce app, a software-as-a-service (SaaS) platform hosted and managed by Salesforce. The bank clarified that the app contains only limited information about its vehicle finance customers and emphasized that its main banking systems remain unaffected. Banking services continue to operate normally.
The bank did not disclose how many records may have been exposed or the specific types of information involved. It partnered with Salesforce in 2024 to digitize the onboarding process for vehicle loan customers, as part of an effort to streamline customer journeys.
Other alleged incidents
In a separate unverified claim, a threat actor using the handle ‘shinymontanna’ listed super administrator access to Vijay Sales’ internal systems for sale at $25,000. The listing allegedly includes access to over 3 million order records, details of 15,000 employees, and billing records for approximately 140,000 vendors. Vijay Sales has not responded to queries about the claim.
Earlier this month, State Bank of India (SBI) reported the exposure of 3,897 customer records on the dark web, including personal information such as mobile numbers, dates of birth, and residential addresses. Meanwhile, cybersecurity company eMudhra announced plans to wind down its global SSL/TLS certificate business following a security incident, though it stated no data was breached.
Salesforce-related risks in focus
This incident follows earlier reports of operational and cultural challenges faced by companies integrating Salesforce’s platforms, including Slack’s struggles post-acquisition. While Salesforce’s SaaS model offers scalability, vulnerabilities in third-party configurations or access controls can expose sensitive data, as alleged in AU Small Finance Bank’s case.
Separately, eMudhra’s decision to exit the SSL/TLS certificate business after browser blocks underscores the risks associated with digital certificate management, though its recent security incident does not appear to involve customer data breaches.
What this means
Lazyfounder analysis — our interpretation, not reported fact.
For founders and operators, this incident underscores the risks of third-party SaaS platforms handling sensitive data. Even if core systems remain secure, a breach in a peripheral app—like AU Small Finance Bank’s Salesforce-based vehicle loan platform—can expose customer records and trigger regulatory scrutiny. The unverified nature of the claims also highlights the challenges of responding to extortion demands from hackers, where negotiation deadlines and public disclosures can escalate reputational damage.
The broader pattern of alleged breaches, including SBI’s dark web exposure and Vijay Sales’ claimed admin access sale, signals a rising trend of cyber threats targeting financial and retail sectors in India. Companies relying on SaaS solutions should audit their vendor configurations, enforce least-privilege access, and prepare incident response plans that address both verified and unverified breach claims.
Related on Lazyfounder
Sources
- Mint (Technology) · 2026-10-30
AU Small Finance Bank data breach: Hackers threaten to leak Aadhaar, PAN and customer records - Inc42 · 2026-10-31
AU SFB Probes Potential Data Leak, Vijay Sales’ Admin Access Allegedly Listed For $25K
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.

About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.
