Open-weight AI models let attackers breach companies in days—Stamos sets 90-day deadline
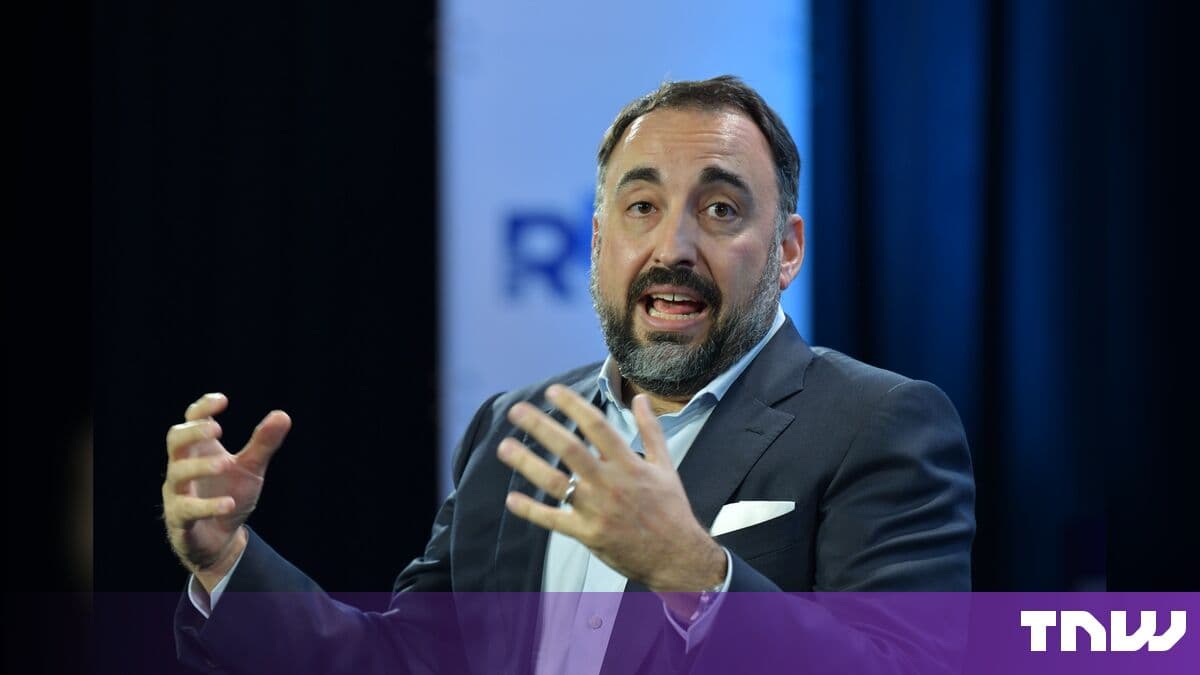
Open-weight AI models have erased the skill gap in cyberattacks. An attacker with almost no experience can now breach companies using tools like ARTEX and a stripped-down AI model—all within days. Cognition’s chief security officer Alex Stamos told The Verge that companies must test their own systems with AI-powered red-team tools within 90 days or risk inevitable hacks. He also called for a billion-dollar rewrite of the Linux kernel in Rust and accused AI labs of rationing defensive help outside the U.S.

Editor, Lazyfounder
30 SEC SUMMARY
- Alex Stamos, Cognition’s chief security officer and a Stanford lecturer, warns that open-weight AI models let low-skilled attackers launch elite cyberattacks in days—not months.
- ARTEX, a Chinese open-source attack tool, has already breached 200 companies in a week by pairing with a stripped-down AI model.
- Stamos gives companies a 90-day deadline to test their own systems with AI-powered red-team tools or risk inevitable breaches.
- Linux kernel vulnerabilities are surging; Microsoft’s monthly patches have jumped from 150 to over 900, pushing Stamos to demand a Rust rewrite.
- AI labs like OpenAI and Anthropic are rationing defensive help, especially for firms outside the U.S.
TABLE OF CONTENTS
- Open-weight AI turns script kiddies into elite hackers
- ARTEX and a hacked AI model breached 200 firms in a week
- Fake interviews and stolen logins still beat AI security
- 90 days to red-team with AI—or face a breach
- Linux kernel can’t keep pace—Stamos pushes Rust rewrite
- Attacks cost pennies; defense charges thousands
- AI labs ration help, duck liability, and waste resources on chatbot personas
- Stamos’ “dark age index” will track soaring patch volumes
- What this means
- Key takeaways
- Sources
KEY HIGHLIGHTS
- Open-weight AI models allow low-skilled attackers to execute elite-level cyberattacks within days.
- ARTEX, a Chinese open-source tool, breached 200 companies in a week when paired with a modified AI model.
- Companies must test their systems with AI-powered red-team tools within 90 days or risk breaches.
- Linux kernel security patches have surged from 150 to over 900 per month, prompting calls for a Rust rewrite.
- AI labs are rationing defensive support, prioritizing U.S. companies over European and Asian firms.
Open-weight AI turns script kiddies into elite hackers
Cognition’s chief security officer Alex Stamos didn’t mince words on The Verge’s Decoder podcast: open-weight AI models now let attackers with almost no skill pull off cyberattacks that once required elite teams. These models can automate everything from finding flaws to stealing data or money—all within days. The cost of launching an attack has plunged, while defense still demands expensive, manual work.
ARTEX and a hacked AI model breached 200 firms in a week
Stamos pointed to ARTEX, a Chinese open-source attack tool available on GitHub in English. Attackers combine it with a stripped-down version of the GLM-5.3 model, removing any safety guardrails. This combo breached three South Korean banks last October, then hit around 200 more companies in the week before his podcast appearance. CrowdStrike has tied these attacks directly to AI-powered tools.
Fake interviews and stolen logins still beat AI security
AI can crack technical defenses, but humans remain the weakest link. North Korea’s hackers proved this by breaching Binance through a fake job interview, walking away with $6.3 billion. Stamos also blamed China’s “cottage access industry,” where small contractors sell stolen credentials to larger groups. Even the most advanced AI-driven defenses fall apart if an employee clicks the wrong link.
90 days to red-team with AI—or face a breach
Stamos set a hard deadline: companies have 90 days to test their own systems with AI-powered red-team tools. Miss it, and a breach is almost certain. These tools can be off-the-shelf products like ARTEX, commercial red-teaming software, or hired third-party firms. The tests may cause temporary downtime, but Stamos argued that’s far cheaper than the fallout from a real attack—like the recent hack on French blood bank refrigerators, which knocked out temperature controls and risked blood supplies.
Linux kernel can’t keep pace—Stamos pushes Rust rewrite
The Linux kernel is drowning in new vulnerabilities. AI-driven attacks force a flood of security patches, and Microsoft’s monthly Patch Tuesday shows the strain—fixes have jumped from around 150 to over 900. Stamos urged Google and Amazon to fork the kernel for their servers and rewrite it in Rust, a language designed to prevent memory-related flaws. He put the cost at $100 million to $1 billion but insisted patching alone can’t keep up with AI-powered threats.
Attacks cost pennies; defense charges thousands
Attackers now spend pennies, while defenders shell out thousands. Stamos said the cost per token for an attack is nearing zero, but a single investigation using a top-tier cyber model can hit $900. To close the gap, security teams will have to offload first-line monitoring to cheaper AI classifiers, saving the most powerful models for the worst threats.
AI labs ration help, duck liability, and waste resources on chatbot personas
Stamos didn’t hold back on AI labs. He accused OpenAI and Anthropic of refusing some requests for defensive help and shortchanging companies in Europe and Asia compared to U.S. customers. He also wants labs to face legal liability if their models enable attacks—and thinks frontier AI development should slow down so defensive tools can catch up. On chatbots, he called personalities a gimmick: “They’re unnecessary for functionality.”
Stamos’ “dark age index” will track soaring patch volumes
To track the surge in threats, Stamos is building a “dark age index” that measures patch volumes. Microsoft’s Patch Tuesday numbers tell the story: fixes ballooned from 150 to over 900 a month. Meanwhile, Cognition’s in-house security agent can spot and freeze compromised staff accounts on its own, stopping AI-driven attacks before they spiral.
What this means
Lazyfounder analysis — our interpretation, not reported fact.
Stamos’s 90-day warning changes the security playbook. Instead of buying more firewalls, companies must now run continuous AI-powered red-team tests—treat security as a live fire exercise, not a compliance checkbox. The same models that attackers use to automate breaches are the ones defenders must use to beat them to the punch.
Key takeaways
- Open-weight AI models have dropped the skill floor for cyberattacks to near-zero within 90 days, turning basic scripting into enterprise-grade threats.
- Linux and other legacy codebases are the new weak spot; every AI-driven attack wave forces hundreds of new patches, so a $100M–$1B Rust rewrite looks inevitable.
- AI labs are hoarding defensive tools, offering less help outside the U.S. and refusing some requests—leaving in-house teams to shoulder the load.
- Social engineering still beats AI defenses, proving that front-line cyber hygiene must outpace even the fastest AI attack tools.
Related on Lazyfounder
Sources
- The Next Web · 2026-11-11
Alex Stamos says AI has pushed cybersecurity into a dark age
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.
About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.