Vanderbilt University Wi-Fi cut after ransomware attack; BYOD claims 1M records stolen
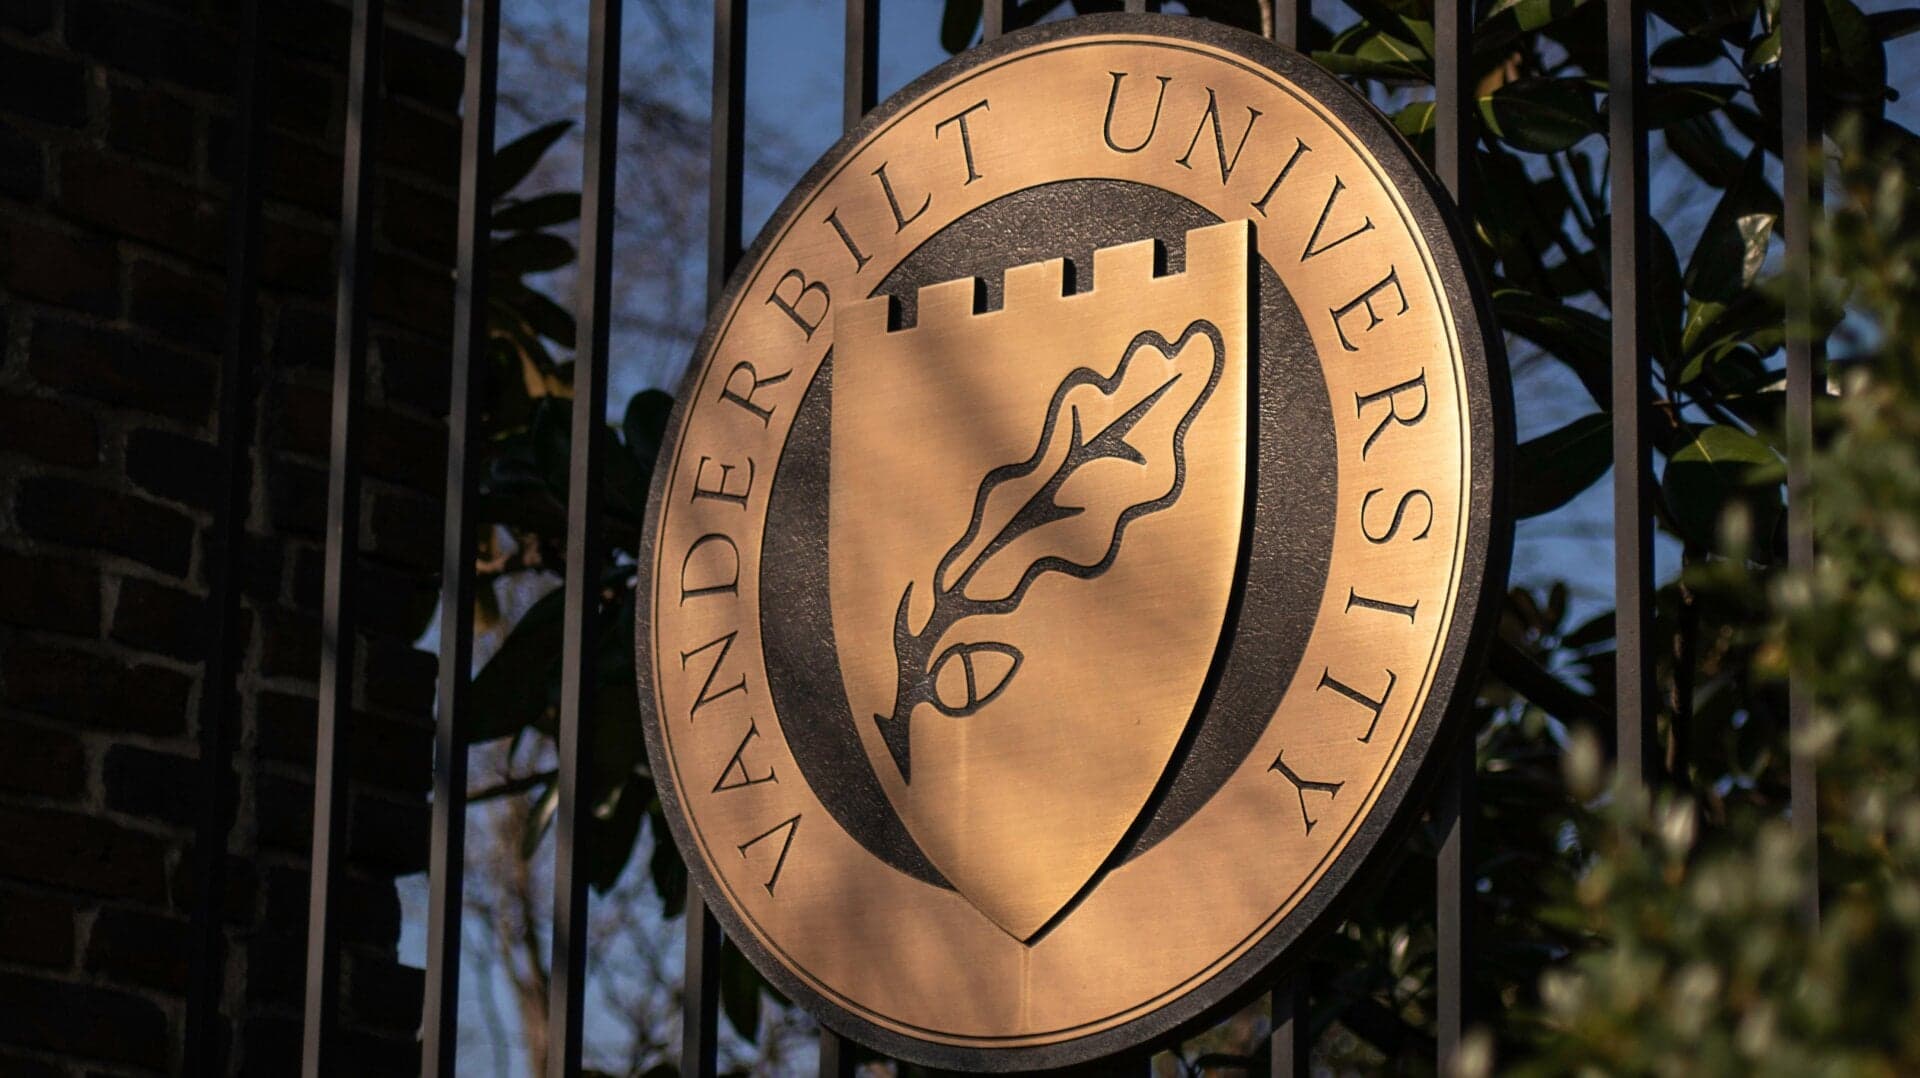
Vanderbilt University cut campus Wi-Fi on November 9 after a likely ransomware attack. The group BYOD says it stole data on more than 1 million people, including Social Security numbers and research files, but the university is still checking the claim. While Wi-Fi returned Monday evening, services like OneDrive and Box stayed dark, leaving students and faculty to scramble for workarounds.

Editor, Lazyfounder
30 SEC SUMMARY
- A ransomware attack hit Vanderbilt University on November 9, knocking out campus Wi-Fi and disrupting classes.
- The group BYOD claims it stole data on over 1 million people, including Social Security numbers and research files, but Vanderbilt hasn’t confirmed this.
- IT teams ordered faculty and students to power down devices and close apps like OneDrive and Microsoft Word to limit damage.
- Some professors canceled classes even as the university insisted operations would continue.
- Wi-Fi was restored by Monday evening, but file-storage services like OneDrive and Box remained offline.
TABLE OF CONTENTS
Campus Wi-Fi goes dark as IT teams scramble to contain breach
Vanderbilt University ordered students and faculty to log off campus Wi-Fi on November 9 after spotting signs of a ransomware attack. IT staff fanned out across Nashville classrooms and dorms, telling professors to power down computers, close Microsoft Word, and exit OneDrive and Dropbox immediately. Some instructors canceled classes on the spot, despite emails from the provost’s office insisting that operations would continue as scheduled.
BYOD claims 1M records stolen—Vanderbilt hasn’t verified the scale
Around noon, pop-ups flooded student desktops, replacing files with a ransom note signed by the group BYOD. The attackers claim they walked away with data on more than 1 million current and former students, staff, and research partners—Social Security numbers, full names, email addresses, phone numbers, employee records, and unpublished research. Vanderbilt has not confirmed the theft; investigators from federal agencies are still combing through logs to verify the group’s claims.
The name BYOD is a smirk at campus policies that encourage students and faculty to connect personal phones and laptops to the university network—a practice that multiplies the number of doors hackers can try.
BYOD’s recent targets: Michigan State, UNM Health, and now Vanderbilt
This is not BYOD’s first strike. In October, Michigan State University faced a similar intrusion, followed by an attack on the University of New Mexico Health System that forced ambulances to reroute and outpatient surgeries to pause. Two weeks after that, Vanderbilt became the latest target, suggesting a pattern aimed at research-rich institutions.
The University of New Mexico Health Sciences Center later said core hospital systems stayed intact, but some staff and student devices were encrypted.
BleepingComputer and Gizmodo both report that BYOD typically publishes stolen data on dark-web leak sites if the victim refuses to negotiate.
Wi-Fi returns but core services remain locked
By Monday evening, Wi-Fi was back and learning platforms like Brightspace and the YES student portal were cleared for use. File-storage services OneDrive and Box, however, stayed offline, stranding homework, grant proposals, and lab notebooks in limbo. Melissa Rose, dean of the Blair School of Music, told students they could ask for deadline extensions while IT teams raced to restore access.
One researcher said she lost everything stored on Vanderbilt’s servers and had to rebuild datasets from personal backups—the kind of disruption that could delay experiments, publications, or even graduation for months.
What this means
Lazyfounder analysis — our interpretation, not reported fact.
Universities keep decades of research, medical records, and personal data in one place—making them prime targets for ransomware gangs that can freeze operations with a single click. When Vanderbilt shut down Wi-Fi, it threw a hard stop on everything from lectures to lab work, showing how quickly even large institutions can be paralyzed.
Key takeaways
- Vanderbilt’s IT team told everyone to disconnect from Wi-Fi and shut down school-issued devices within hours of detecting the attack, a standard playbook to contain ransomware.
- The group BYOD has hit at least three universities and health systems in recent weeks, suggesting a coordinated campaign against research-heavy targets.
- While Wi-Fi and learning platforms came back online quickly, file-storage services like OneDrive and Box stayed dark, leaving students and researchers without access to critical documents for days.
- Policies that let students and faculty use their own laptops and phones broaden the attack surface, giving hackers more entry points into university networks.
Related on Lazyfounder
Sources
- Gizmodo · 2026-11-09
Attackers Claim to Have Stolen Data on Over 1 Million Vanderbilt Students and Staff - Mashable · 2026-11-10
Vanderbilt University cyberattack: What we know
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.
About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.