Travelodge security failures led to assault, review finds
Travelodge is facing criticism after an independent review revealed systemic security failures that enabled a sexual assault at one of its hotels. The review, commissioned following the 2022 incident, found the company’s policies were inadequate and called for urgent reforms, including ID checks for room keys and a new policy on violence against women and girls.

Editor, Lazyfounder
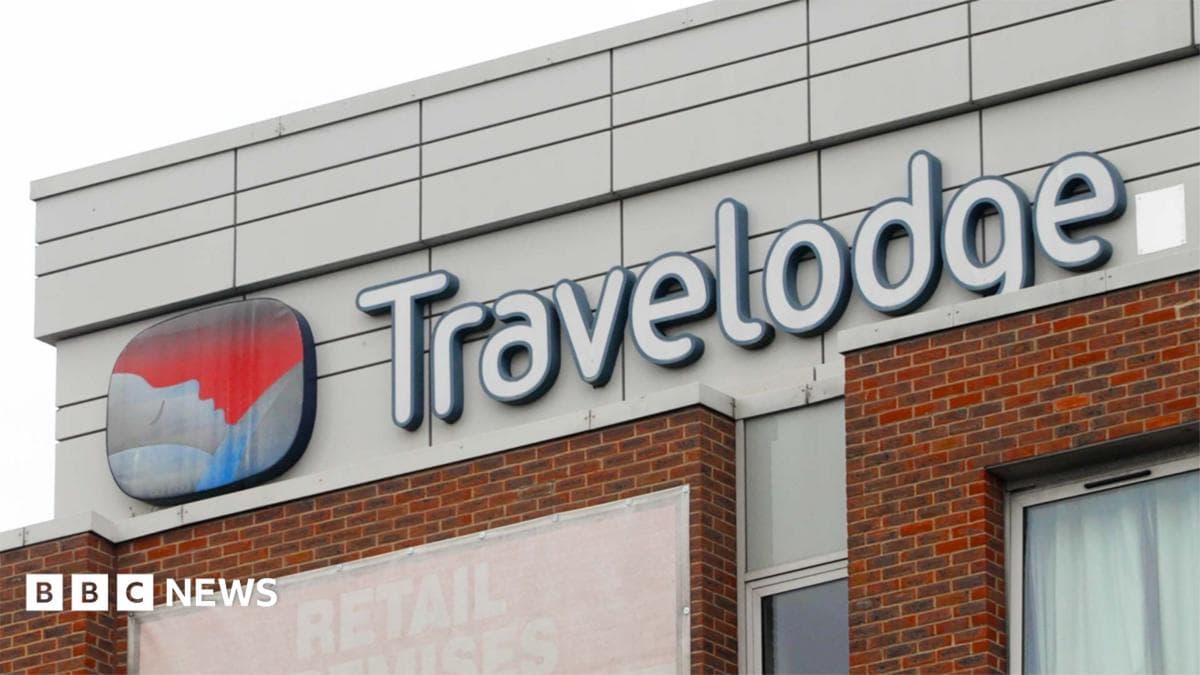
Travelodge is facing criticism after an independent review revealed systemic security failures that enabled a sexual assault at one of its hotels. The review, commissioned following the 2022 incident, found the company’s policies were inadequate and called for urgent reforms, including ID checks for room keys and a new policy on violence against women and girls.
30 SEC SUMMARY
- Travelodge faces scrutiny after an independent review found its security policies failed a sexual assault victim at its Maidenhead hotel.
- The attacker gained access to the victim’s room after hotel staff provided a key without proper verification.
- The review identified systemic security flaws, including no policy on violence against women and girls at the time.
- Travelodge has begun trials of ID checks for room keys and is implementing 38 recommended reforms.
- Former CEO Jo Boydell stepped down in August 2026 amid criticism over handling of safety complaints.
TABLE OF CONTENTS
- Security Failures at Travelodge
- Systemic Issues Identified
- Leadership and Policy Changes
- What this means
- Key takeaways
- FAQ
- Sources
KEY HIGHLIGHTS
- An independent review concluded Travelodge’s security policies were 'not fit for purpose' after an attacker was given a key to a guest’s room.
- The review revealed nearly one in 10 Travelodge hotels reported room intrusions during the summer of 2026.
- Travelodge had no policy on violence against women and girls at the time of the incident, prompting urgent reforms.
- Former CEO Jo Boydell resigned in August 2026 amid criticism over the company’s handling of safety complaints.
- The company is trialling ID checks for room keys and implementing 38 recommendations to improve security.
Security Failures at Travelodge
An independent review, led by barrister Paul Greaney KC, found that Travelodge’s security policies were 'not fit for the purpose of keeping guests safe' at the time of a sexual assault at its Maidenhead hotel in December 2022. According to BBC News (Tech & Business), the attacker, Kyran Smith, was able to obtain a key to the victim’s room by falsely claiming to be her boyfriend.
The receptionist who handed over the key had received no training in key security, a lapse that contributed to the incident.
Systemic Issues Identified
The review highlighted broader security failures across Travelodge’s operations. Nearly one in 10 Travelodge hotels reported room intrusions during the summer of 2026, according to the findings. Mystery shoppers testing security at five hotels, including the Maidenhead location, were able to access guest rooms through housekeeping staff without being sent to reception or asked for identification.
At the time of the review, Travelodge had no policy addressing violence against women and girls, a gap the report described as unacceptable.
Leadership and Policy Changes
The review made 38 recommendations to overhaul Travelodge’s security policies. These include requiring ID checks for guests requesting room keys and equipping reception staff with body-worn cameras. Since May 2026, the company has been trialling ID checks at select hotels.
Former CEO Jo Boydell stepped down in August 2026 following criticism of how the company handled safety complaints. Boydell stated she only became aware of the assault during the court case nearly three years after the incident. Interim Chief Executive Ray Reidy has since apologized 'unreservedly' to the victim.
The victim reported that her complaint email was handled by Boydell’s office without her direct knowledge, and the customer services team offered a refund of £30, which she described as inadequate given the circumstances.
What this means
Lazyfounder analysis — our interpretation, not reported fact.
This incident and the subsequent review expose critical gaps in corporate accountability within the hospitality industry, particularly around guest safety. For founders and operators, the Travelodge case serves as a stark reminder that operational policies—especially those involving security—must be regularly audited and updated to reflect real-world risks. The fact that nearly one in 10 Travelodge hotels reported room intrusions in a single summer suggests a sector-wide issue, not an isolated failure.
For startups in hospitality or shared spaces, this highlights the need for proactive risk assessment, staff training, and clear policies on violence and discrimination. The review’s recommendations, such as ID checks and body-worn cameras, may seem burdensome, but they reflect a growing expectation that companies prioritize safety over convenience. Ignoring these issues can lead to reputational damage, legal liability, and leadership turnover—as seen with Travelodge’s former CEO.
Finally, this case underscores the importance of transparency with customers, particularly when things go wrong. A refund offer, while standard, can feel tone-deaf in the wake of a traumatic incident. How companies respond to crises often defines their long-term trust with customers.
Key takeaways
- Travelodge’s security policies were deemed 'not fit for purpose' after an attacker obtained a key to a guest’s room without verification.
- The independent review identified systemic flaws, including no policy on violence against women and girls at the time of the incident.
- Nearly one in 10 Travelodge hotels reported room intrusions during the summer of 2026, pointing to broader security issues.
- The review made 38 recommendations, including ID checks for room keys and body-worn cameras for staff.
- Former CEO Jo Boydell resigned in August 2026 following criticism over the company’s handling of safety complaints.
- Travelodge has begun trialling ID checks for room keys at select hotels as part of its reforms.
FAQ
What happened at the Travelodge hotel in Maidenhead?
In December 2022, a woman was sexually assaulted at a Travelodge hotel in Maidenhead after an attacker obtained a key to her room by falsely claiming to be her boyfriend. The incident exposed significant flaws in the hotel’s security policies.
What did the independent review find?
The review, led by barrister Paul Greaney KC, concluded that Travelodge’s security policies were 'not fit for purpose.' It identified systemic issues, including a lack of training for staff, no policy on violence against women and girls, and widespread reports of room intrusions across the hotel chain.
What changes is Travelodge making after the review?
Travelodge is implementing 38 recommendations from the review, including trialling ID checks for room keys, introducing body-worn cameras for reception staff, and developing a policy on violence against women and girls in collaboration with the Suzy Lamplugh Trust.
Why did Travelodge’s former CEO step down?
Jo Boydell resigned in August 2026 amid criticism over the company’s handling of safety complaints, including the incident at the Maidenhead hotel. She stated she only became aware of the assault during the court case nearly three years later.
Are room intrusions a common problem in hotels?
The review suggested that room intrusions are a sector-wide issue, reporting that nearly one in 10 Travelodge hotels experienced such incidents during the summer of 2026.
Related on Lazyfounder
Sources
- BBC News (Tech & Business) · 2026-10-01
Travelodge failed Maidenhead sex assault victim 'at every stage'
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.
About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.