
InfoScale urges enterprises to prioritize runtime resilience over disaster recovery
Cloud Software Group Inc.’s InfoScale division is advocating for enterprises to move beyond traditional disaster recovery and prioritize runtime resilience. The shift comes as AI-driven cyber threats and automation expose vulnerabilities in business continuity, turning downtime into a multi-dimensional risk that includes regulatory exposure, financial loss, and customer churn.

Editor, Lazyfounder
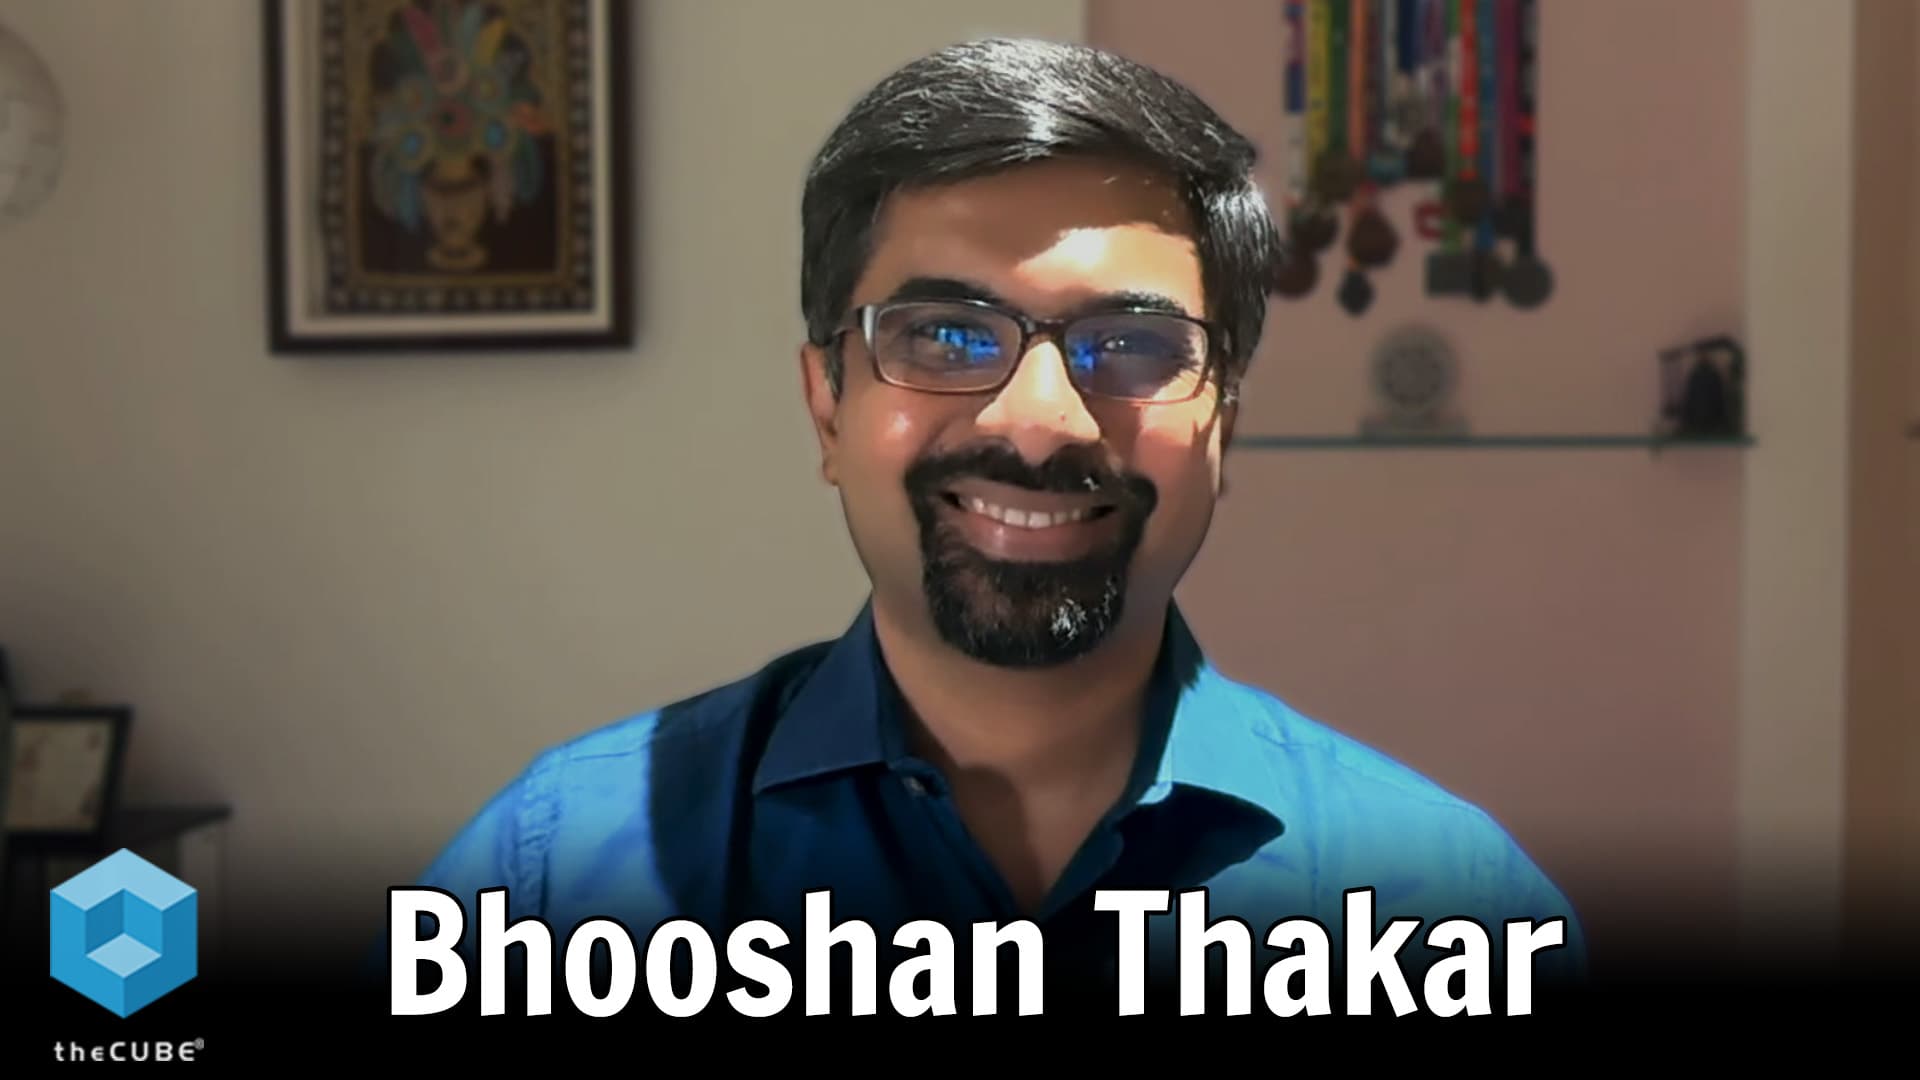
TABLE OF CONTENTS
Why runtime resilience matters now
Traditional disaster recovery frameworks focus on restoring servers, storage, and networks, but these measures often fail to ensure operational continuity during disruptions. According to SiliconANGLE, enterprises now face AI-driven cyber threats and automated attacks that accelerate the need for real-time resilience.
Bhooshan Thakar, Senior Vice President and General Manager of InfoScale at Cloud Software Group, emphasized the gap between infrastructure survival and operational viability. He stated that while infrastructure may recover, the operational state—the live environment where business applications run—often does not. This disconnect leaves enterprises exposed to regulatory risks, financial penalties, and customer attrition.
The limits of cloud resilience guarantees
Cloud service providers ensure the resiliency of their infrastructure, but application owners retain responsibility for resilience within the cloud. SiliconANGLE reports that this division of accountability often creates a false sense of security, as business applications rely on interconnected layers—databases, middleware, and APIs—that must function cohesively.
If any layer fails or data integrity is compromised, the entire stack can collapse even if the underlying infrastructure reports as healthy. Thakar noted that runtime resilience platforms must track dependencies, runtime states, and data integrity in real time to prevent such failures.
AI as both threat and tool
AI-driven cyber threats are accelerating the cycle of security updates and patching for enterprises. SiliconANGLE highlighted that businesses once conducted planned failovers every six months, but now many patch business-critical applications daily or weekly to mitigate risks.
To counter these threats, Cloud Software Group joined Anthropic PBC’s Project Glasswing in June. The collaboration uses Anthropic’s Claude Mythos Preview model for security work, signaling a shift toward AI-powered resilience tools. However, Thakar cautioned that AI also introduces new attack surfaces, requiring enterprises to validate business transaction continuity—not just infrastructure restoration—during disruptions.
How enterprises are adapting
Enterprises are redefining how they measure downtime. Instead of tracking the time to restore a virtual machine, many now focus on the time to achieve the first validated, clean business transaction after a disruption. This metric reflects the broader impact of downtime, including regulatory exposure and lost customer trust.
Thakar described this evolution as a move from preventing failures to ensuring businesses can operate through them. He stated that traditional investments in prevention and recovery leave critical gaps in resilience, particularly as AI-driven automation reshapes threat landscapes.
What this means
Lazyfounder analysis — our interpretation, not reported fact.
This shift in enterprise resilience strategies reflects a broader trend: the decoupling of infrastructure reliability from business continuity. For founders and operators, particularly in sectors with stringent regulatory requirements like finance or healthcare, the implications are clear. Runtime resilience is no longer a technical nicety but a business imperative.
The emphasis on real-time tracking of dependencies and data integrity also underscores the need for platforms that can operate alongside live applications, rather than merely restoring them. This could accelerate demand for tools like InfoScale, as well as AI-driven solutions that can detect and mitigate threats dynamically. For startups building in cloud-native environments, the message is equally relevant: assume that cloud providers’ infrastructure guarantees are necessary but insufficient. The onus is on application owners to ensure their stacks—and the business processes they enable—can withstand disruptions without relying solely on recovery playbooks.
Related on Lazyfounder
Sources
- SiliconANGLE · 2026-10-28
Why InfoScale wants enterprises to protect live operations, not just servers
This story is an original summary drafted with AI by Lazyfounder from the reporting listed above and checked by automated validation. Facts are attributed to their original publishers; sections marked as analysis are Lazyfounder's. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links, and see our AI policy and corrections policy.

About the author
Editor, Lazyfounder
Tarun Mottlia edits LazyFounders, covering Indian startups, funding rounds, AI and product launches. Every story on the site is AI-assisted and checked against its cited sources before publication.
More stories by Tarun MottliaGet the LazyFounder Brief
Startup, funding and AI news in a five-minute read. Join the early-access list.
